FTA – Fault Tree Analysis: How to Go from Top Event to Root Causes?
FTA begins with the scenario that must not happen and drills down step by step to the basic failures causing it. This is how to build a correct tree, calculate probabilities, and find the system's weak points.
In this insight you will learn
- What FTA is and how it differs from FMEA
- How to properly define a top event and set analysis boundaries
- What AND and OR gates mean and how to calculate probabilities through them
- What Minimal Cut Sets are and why they are the most important output of the tree
- Which common mistakes turn a fault tree into a pretty diagram without value
Fault Tree Analysis starts from the scenario that must not happen and drills down step by step to the basic failures causing it. This is how to build a correct tree, calculate probabilities, and identify the system's weak points.
What is FTA?
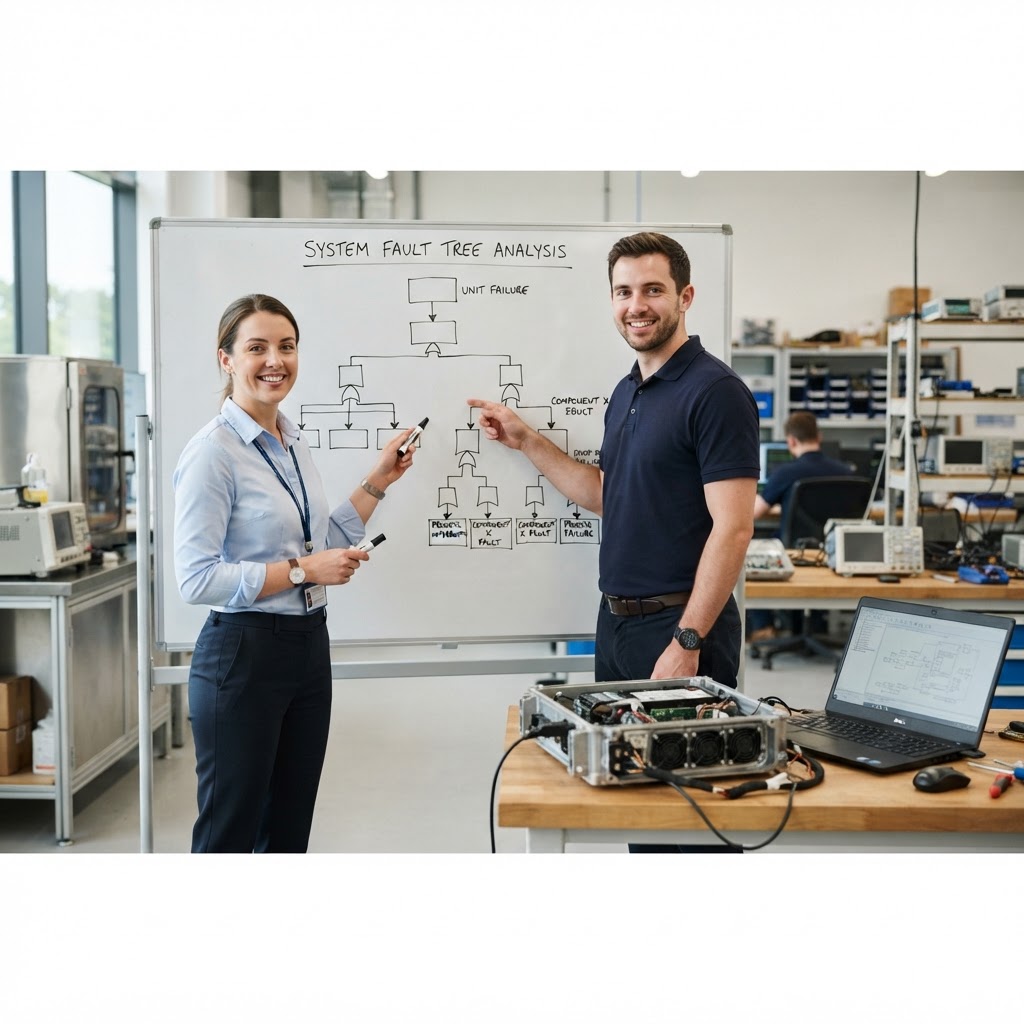
FTA (Fault Tree Analysis) is a deductive, top-down method. You start with one undesired event, known as the Top Event, and ask repeatedly: What must happen for this to occur? Each answer becomes a branch, and the branches split until they reach basic events – component failures, human errors, or environmental conditions – which no longer need to be broken down.
The method was developed in the early 1960s at Bell Labs to evaluate the safety of missile launch systems for the US Air Force, and has since become a key tool in aviation, nuclear industry, railways, defense, and medical devices. The international standard IEC 61025 defines the principles and symbols of the method, and the Fault Tree Handbook published by the US Nuclear Regulatory Commission (NUREG-0492) is still a widely accepted reference. In civil aviation, FTA is one of the tools used in the safety assessment process according to SAE ARP4761A.
FTA vs. FMEA – Not a Substitute, But a Complement
FMEA works bottom-up: you take every component or process step and ask what happens if it fails. FTA works in the opposite direction: you take one severe result and ask what could cause it.
The fundamental difference:
- FMEA excels in broad coverage – it covers all failure modes, even those with small impacts.
- FTA excels in depth – it focuses on one scenario and reveals combinations of failures. A single failure in FMEA might seem negligible, but in the tree, you see that combined with another failure, it leads to a catastrophe.
In complex projects, both are used: FMEA identifies the failure modes, and FTA is used to analyze the most severe events that emerged from it or from risk analysis.
Step 1: Defining the Top Event
This is the stage where most trees fail. A good top event is specific, measurable, and bounded:
- Poor: "The system is not working."
- Good: "Loss of cooling to the control unit during operation, for more than 60 seconds."
Alongside the top event, you define the analysis boundaries: which subsystems are included, in what operating state, and what assumptions are made (e.g., whether operator errors are considered). Without clear boundaries, the tree expands infinitely.
Step 2: Building the Tree – Logical Gates
The tree is built from events connected by logical gates. The two basic gates are:
- OR Gate – The output event occurs if at least one of the input events occurs. This is the gate for single points of failure.
- AND Gate – The output event occurs only if all input events occur together. This is the gate for redundancy.
An important working rule: move down only one level at a time. If you skip directly from the top event to component failures, you miss intermediate mechanisms – exactly the place where common-cause failures hide.
Step 3: Calculating Probabilities
Once each basic event has a probability, the probability of the top event can be calculated (assuming independent events):
- AND Gate: Multiply the probabilities. P = P1 × P2
- OR Gate: P = 1 – (1 – P1)(1 – P2). When probabilities are small, it is customary to use the approximation P ≈ P1 + P2.
Probabilities for basic events come from field data, supplier data, or predictive models. This is where the link to other reliability analyses comes in: a failure rate or a Weibull distribution of a component becomes a probability of failure over a defined mission time.
Step 4: Minimal Cut Sets – The Truly Important Output
A Cut Set is a combination of basic events whose joint occurrence causes the top event. A Minimal Cut Set is a combination from which no event can be removed without the top event ceasing to occur.
Why is this important?
- First-order Cut Set (a single event only) is a single point of failure. Each such item is an immediate suspect.
- Second-order Cut Sets and above show where redundancy works, and where it only seems to work.
- Ranking Cut Sets by their contribution to the total probability shows where every dollar invested will yield the most improvement.
Practical Example: Loss of Cooling in an Electronic Unit
A manufacturer of an electronic unit for an airborne system designed cooling with two fans in redundancy, to meet a safety requirement. The team assumed the redundancy solved the problem.
The tree built for the "Loss of Cooling" top event looked like this:
- Top OR gate with two branches:
- Both fans failed (AND gate). If the failure probability of each fan during the mission is 0.01, the probability for both together is 0.0001.
- Loss of power supply to the fans – one power supply feeding both, with a failure probability of 0.001.
The probability of the top event: approximately 0.0011. Meaning, more than 90% of the risk comes from the common power supply, which is a first-order Cut Set. The redundancy in the fans was real, but the common power supply negated most of its benefit.
The solution was not a third fan, but separating the power supply into two channels. This is exactly the kind of insight that FTA provides and that is hard to see in an FMEA table, where each component is examined separately.
Common Mistakes
- Too general top event – The tree becomes huge and unusable.
- Ignoring Common Cause failures – Assuming independence between components that share a power supply, software, environment, or maintenance creates overly optimistic results.
- Omitting human and software errors – because they are hard to quantify. Even if not quantified, they should be shown in the tree.
- A tree built once and forgotten – FTA needs to be updated with design changes and field failure data, for example from a FRACAS system.
- Focusing on the final number – The primary value is in the Cut Sets and understanding the mechanism, not just the probability of the top event.
Summary
FTA starts with the most important question: What must not happen? From there, it builds, using the simple logic of AND and OR gates, all the paths leading to this event, allowing for probability calculation and identification of the combinations that contribute most to it.
The true value of the method is not in the diagram itself, but in the insights: hidden single points of failure, redundancy that is not truly independent, and design decisions where a small investment significantly reduces risk.
A good fault tree complements FMEA, relies on real reliability data, and is updated throughout the product's lifecycle. Thus, it transforms from a document requirement into an engineering team tool.
Want to go deeper into reliability and failure analysis?
FTA, FMEA, and quantitative reliability analysis are key parts of the CRE certification body of knowledge. In the ALD Academy preparation course, you learn to build and analyze them in a practical way.
Related Knowledge Centers
FMEA – Identify the failure before it happens
RAMS – What is it, and how to build a RAMS plan that works in a project
Insight from Dr. Zigmond Bluvband
“Quality is not created in the final inspection. It is created in the decisions made at the beginning of the project.”
This insight is based on professional knowledge, practical experience and study materials of ALD Advanced Solutions, and inspired by the books and publications of Dr. Zigmond Bluvband.