Risk Management – How to Build a Process That Works Throughout the Project, Rather Than a Table Forgotten in a Drawer?
Effective risk management is an ongoing process, not a one-off document. This is how to define criteria, assess risks in a matrix, choose a treatment option, and run a risk register that shapes real decisions.
In this insight you will learn
- What risk is according to ISO 31000, and why it is not merely "something bad that might happen"
- What the stages of the risk management process are, from establishing context through monitoring and reporting
- How to build a usable risk matrix and avoid its pitfalls
- What treatment options exist, and when it is right to accept a risk instead of treating it
- How FMEA, FTA and other tools fit into the overall process
Every engineering project begins with uncertainty: a new supplier, an untested technology, a tight schedule, or a customer requirement that has not yet been clarified. The question is not whether risks will exist, but whether the organization identifies them in time, understands which of them truly matter, and makes informed decisions about them.
What Is Risk?
ISO 31000:2018 defines risk as the effect of uncertainty on objectives. This definition has two practical consequences:
- Risk is always tied to an objective. There is no such thing as a "general risk". There is risk to meeting the schedule, to safety requirements, to the budget, or to the reliability target. If the objective is not defined, the risk is not truly defined either.
- The effect can also be positive. Uncertainty can create opportunity, which is why ISO 9001:2015 speaks in clause 6.1 of "risks and opportunities" and not of risks alone.
In practice, most organizations assess risk through two dimensions: the likelihood that the event will occur and the severity of the consequence if it does. A low-likelihood event can still be critical if its consequence is severe.
The Process: Six Components That Work Together
ISO 31000 is a guidelines standard, not a requirements standard, and therefore does not prescribe a single method. It describes a process that can be adapted to any organization and any project:
1. Communication and Consultation
Risks are identified better when the people who know the details are involved in the process: design, manufacturing, procurement, service and the customer. A project manager who identifies risks alone will mainly identify schedule risks.
2. Defining Scope, Context and Criteria
Before identifying a single risk, decide what is being examined, what the objectives are, and what will count as a "high" risk. This is the stage most organizations skip, and the reason the same risk receives a different score from different people.
3. Risk Assessment
The assessment comprises three steps:
- Identification – what might happen, why and how.
- Analysis – what the likelihood is, what the consequence is, and which controls already exist.
- Evaluation – comparison against the criteria and a decision on which risks require treatment and in what order.
4. Risk Treatment
Selecting the treatment option and implementing it (see below).
5. Monitoring and Review
Periodic review: were the mitigation actions carried out, do they work, and which new risks have been added.
6. Recording and Reporting
Documenting the decisions and passing the picture to those who make decisions. Reporting that never reaches management has no effect on resource allocation.
The Risk Matrix – A Useful Tool With Pitfalls
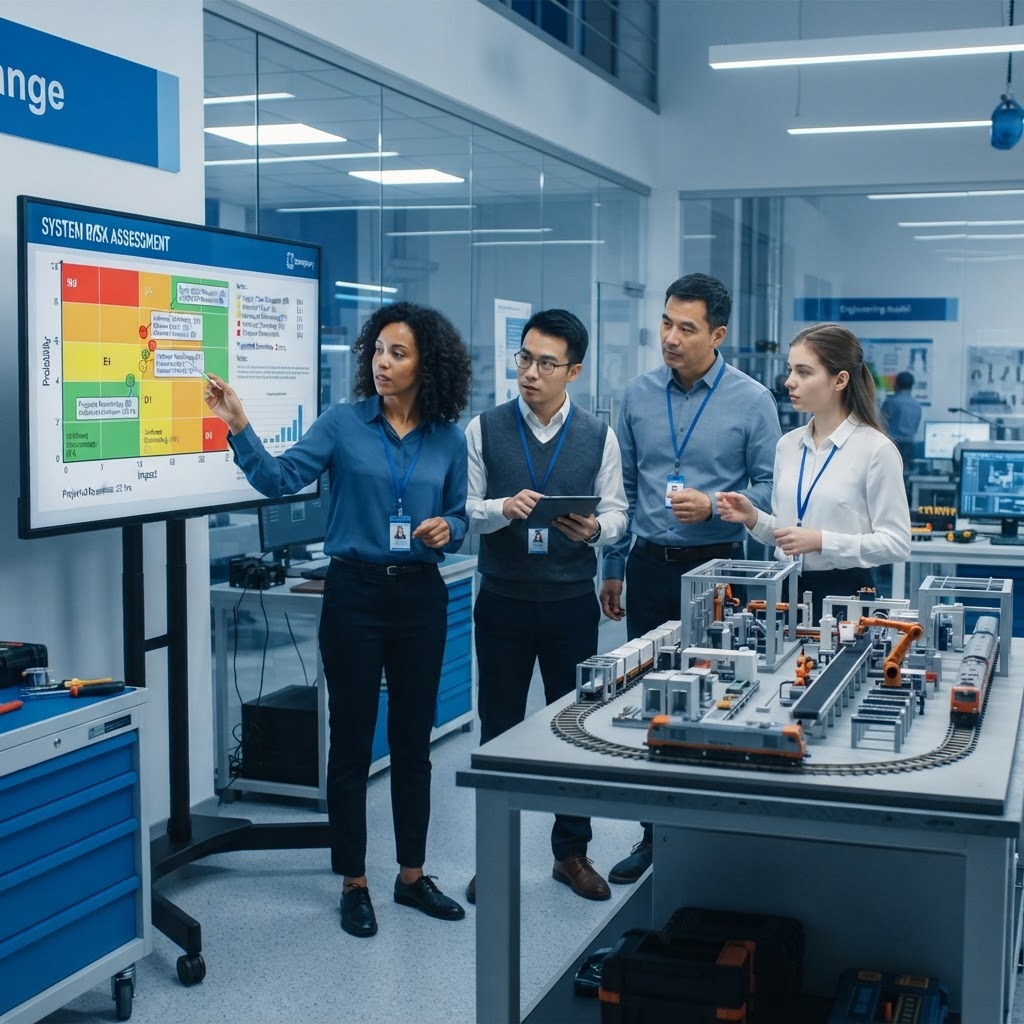
The likelihood–severity matrix is the most common prioritization tool, because it is simple and understood by everyone. For it to work:
- Define every level in words and in numbers. "High likelihood" must be defined, for example as a frequency or probability range, and not be a matter of feeling.
- Define severity for each type of objective. A two-week delay and a safety incident are not on the same scale. Many organizations define a separate severity table for safety, schedule, cost and reputation.
- Do not settle for the product of the two. A risk with catastrophic severity and low likelihood may receive the same score as a moderate and frequent risk, even though they require completely different decisions. It is therefore common practice to rule that top-level severity requires review in every case.
- Remember that this is an assessment. The matrix organizes the thinking, but it does not replace engineering analysis.
Risk Treatment Options
ISO 31000 presents several treatment options, and not all of them mean "do more actions":
- Avoidance – not starting or not continuing the activity that creates the risk, for example foregoing an immature technology.
- Removing the risk source or changing the likelihood – design change, additional inspection, qualification of an additional supplier.
- Changing the consequence – redundancy, contingency plan, safety stock.
- Sharing or transferring – a contract, insurance, or allocation of responsibility with a partner.
- Retaining the risk – a conscious, documented decision not to treat it, because the risk falls within the criteria or the cost of treatment exceeds the benefit.
- Taking a risk in order to pursue an opportunity – when the potential justifies it.
Accepting a risk is a legitimate decision, provided it is made by someone authorized to make it and is documented. "We did not treat it because we ran out of time" is not acceptance of a risk.
The Risk Register
The risk register is where the process becomes routine work. A good register includes, for each risk:
- A description in the form cause → event → consequence
- The objective it affects
- Likelihood and severity rating before and after treatment
- Treatment actions, owner and target date
- Status and the date of the next review
The most important rule: every risk has an owner. A risk that "belongs to everyone" is treated by no one.
How Do FMEA, FTA and Other Tools Fit In?
Risk management is the framework. The engineering tools are the way to perform the assessment in depth where it is required:
- FMEA – a bottom-up analysis of failure modes in the design or the process.
- FTA – a top-down analysis, from an undesired top event to its causes.
- Hazard Analysis – identification and assessment of safety hazards, mainly in RAMS projects.
- Bow-Tie – presentation of causes, event and consequences together with the preventive and mitigating barriers.
IEC 31010:2019 consolidates a wide range of risk assessment techniques and helps select the one suited to each situation. The main findings of every analysis should be transferred to the risk register, so that they receive an owner, a decision and follow-up.
An Industry Example
An electronics company developing an assembly for a defense customer maintained a risk table that had been prepared at the start of the project and was never updated. In the second half of development it emerged that a key component was approaching end of production, and the issue surfaced only when procurement tried to order it.
On the next project the team changed the method: criteria for likelihood and severity were defined in advance, procurement and the supply chain were brought into the risk identification workshop, an owner was assigned to every risk, and a review was set at every milestone. The component obsolescence risk was identified already at the design stage, and an alternative component and advance purchase were evaluated up front. The DFMEA findings were transferred to the register, and management received an up-to-date risk picture at every project review.
Common Mistakes
- Managing risks only at the start of the project
- Rating without defined criteria
- Focusing only on technical risks, without suppliers, personnel and schedules
- Risks without owners and without target dates
- Ignoring opportunities
- A register that no one uses to make decisions
Summary
Risk management is not a table filled in to satisfy a requirement. It is a process that begins with defining objectives and criteria, continues with identifying and assessing what might affect them, and ends with decisions: treat, transfer, avoid or accept.
Engineering tools such as FMEA and FTA provide depth. The framework provides consistency, ownership and follow-up. An organization that combines both gets fewer surprises and a better ability to explain to the customer and to management why each decision was made.
Want to Go Deeper into Risk Management?
Risk management at the organizational and project level is an essential part of the role of a manager of quality and organizational excellence. In the ALD Academy CMQ/OE course you learn the tools and frameworks for managing quality at the managerial level, as preparation for the international certification.
Related Insights
FMEA – Identifying the failure before it happens
FTA – Fault Tree Analysis: How to go from the top event to root causes?
Insight from Dr. Zigmond Bluvband
“Risk management does not predict the future. It prepares the organization for any possible future.”
This insight is based on professional knowledge, practical experience and study materials of ALD Advanced Solutions, and inspired by the books and publications of Dr. Zigmond Bluvband.